

毎月、GOWUKAKUは1500人以上の受験者が試験準備を助けて、試験に合格するために受験者にご協力します
Fortinet NSE 6 - FortiWeb 6.1 試験
最新更新時間: 2026/09/21
【秋学習応援セール|10月限定キャンペーン】:NSE6_FWB-6.1 最新真題を買う時、日本語版と英語版両方を同時に獲得できます。
実際の問題集を練習し、試験のポイントを了解し、テストに申し込むするかどうかを決めることができます。
さらに試験準備時間の35%を節約するには、NSE6_FWB-6.1 問題集を使用してください。
Question No : 1
True transparent proxy mode is best suited for use in which type of environment?
正解:
Explanation:
Does not require changes to the IP address scheme of the network. Requests are destined for a web server and not the FortiWeb appliance. This operation mode supports the same feature set as True Transparent Proxy mode.
Reference: https://docs.fortinet.com/document/fortiweb/6.3.0/administration-guide/211763/planning-the-network-topology
Question No : 2
When is it possible to use a self-signed certificate, rather than one purchased from a commercial certificate authority?
正解:
Explanation:
This can include SSL/TLS certificates, code signing certificates, and S/MIME certificates. The reason why they’re considered different from traditional certificate-authority signed certificates is that they’re created, issued, and signed by the company or developer who is responsible for the website or software being signed. This is why self-signed certificates are considered unsafe for public-facing websites and applications.
Reference: https://sectigostore.com/page/what-is-a-self-signed-certificate/
Question No : 3
Which algorithm is used to build mathematical models for bot detection?
正解:
Explanation:
FortiWeb uses SVM (Support Vector Machine) algorithm to build up the bot detection model
Reference: https://docs.fortinet.com/document/fortiweb/6.3.7/administration-guide/193258/machine-learning
Question No : 4
Which statement about local user accounts is true?
正解:
Explanation:
You can configure the Remedy Single Sign-On server to authenticate TrueSight Capacity Optimization users as local users.
Reference: https://docs.bmc.com/docs/TSCapacity/110/setting-up-local-user-authentication-in-remedy-sso-743238341.html
Question No : 5
Refer to the exhibit.
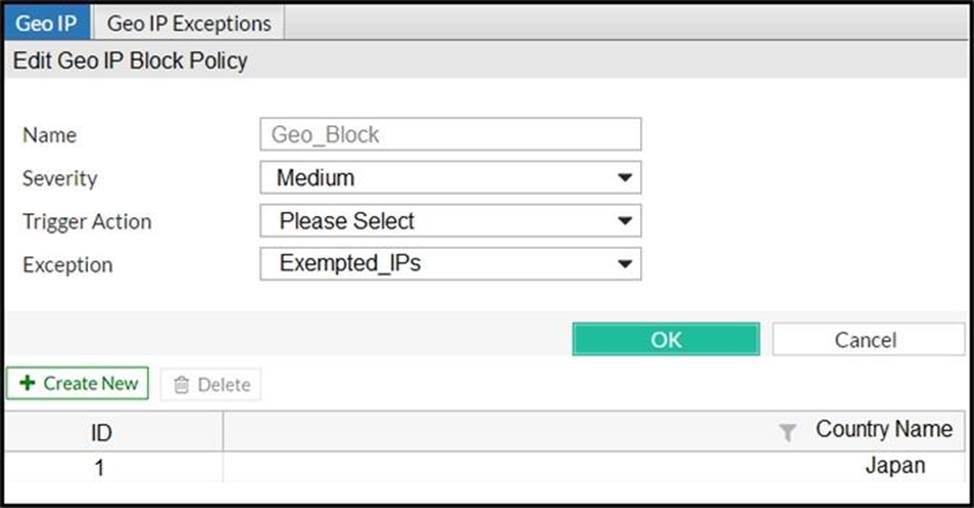
FortiWeb is configured to block traffic from Japan to your web application server. However, in the logs, the administrator is seeing traffic allowed from one particular IP address which is geo-located in Japan.
What can the administrator do to solve this problem? (Choose two.)
正解:
Explanation:
IP reputation leverages many techniques for accurate, early, and frequently updated identification of compromised and malicious clients so you can block attackers before they target your servers.
IP blacklisting is a method used to filter out illegitimate or malicious IP addresses from accessing your networks. Blacklists are lists containing ranges of or individual IP addresses that you want to block.
Reference:
https://docs.fortinet.com/document/fortiweb/6.3.5/administration-guide/137271/blacklisting-whitelisting-clients
https://www.imperva.com/learn/application-security/ip-blacklist/
Question No : 6
What is one of the key benefits of the FortiGuard IP reputation feature?
正解:
Explanation:
FortiGuard IP Reputation service assigns a poor reputation, including virus-infected clients and malicious spiders/crawlers.
Reference: https://docs.fortinet.com/document/fortiweb/6.1.1/administration-guide/137271/blacklisting-whitelisting-clients
Question No : 7
How does FortiWeb protect against defacement attacks?
正解:
Explanation:
The anti-defacement feature examines a web site’s files for changes at specified time intervals. If it detects a change that could indicate a defacement attack,
the FortiWeb appliance can notify you and quickly react by automatically restoring the web site contents to the previous backup.
Reference: https://help.fortinet.com/fweb/551/Content/FortiWeb/fortiweb-admin/anti_defacement.htm
Question No : 8
Review the following configuration:
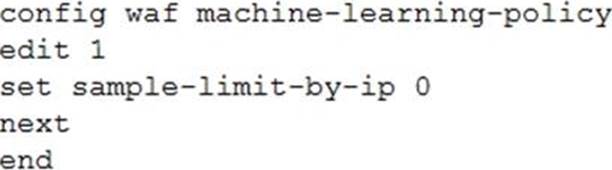
What is the expected result of this configuration setting?
正解:
Question No : 9
What can an administrator do if a client has been incorrectly period blocked?
正解:
Explanation:
Block Period
Enter the number of seconds that you want to block the requests. The valid range is 1C3,600 seconds. The default value is 60 seconds.
This option only takes effect when you choose Period Block in Action.
Note: That’s a temporary blacklist so you can manually release them from the blacklist.
Reference: https://docs.fortinet.com/document/fortiweb/6.3.1/administration-guide/600188/configuring-bot-detection-profiles
Question No : 10
What role does FortiWeb play in ensuring PCI DSS compliance?
正解:
Explanation:
FortiWeb protects against attacks that lead to sensitive data exposure such as SQL Injection and other injection types. Additionally, FortiWeb inspects all web server outgoing traffic for sensitive data such as Social Security numbers, credit card numbers and other predefined or custom based sensitive data.
Reference: https://www.gordion.de/fileadmin/user_upload/SG-PCI-Compliance.pdf